cloudtec is certified to ISO/IEC 27001
Our data protection processes are documented, controlled and verified by an independent audit. How we got there, including the stretches that were not entirely straightforward.
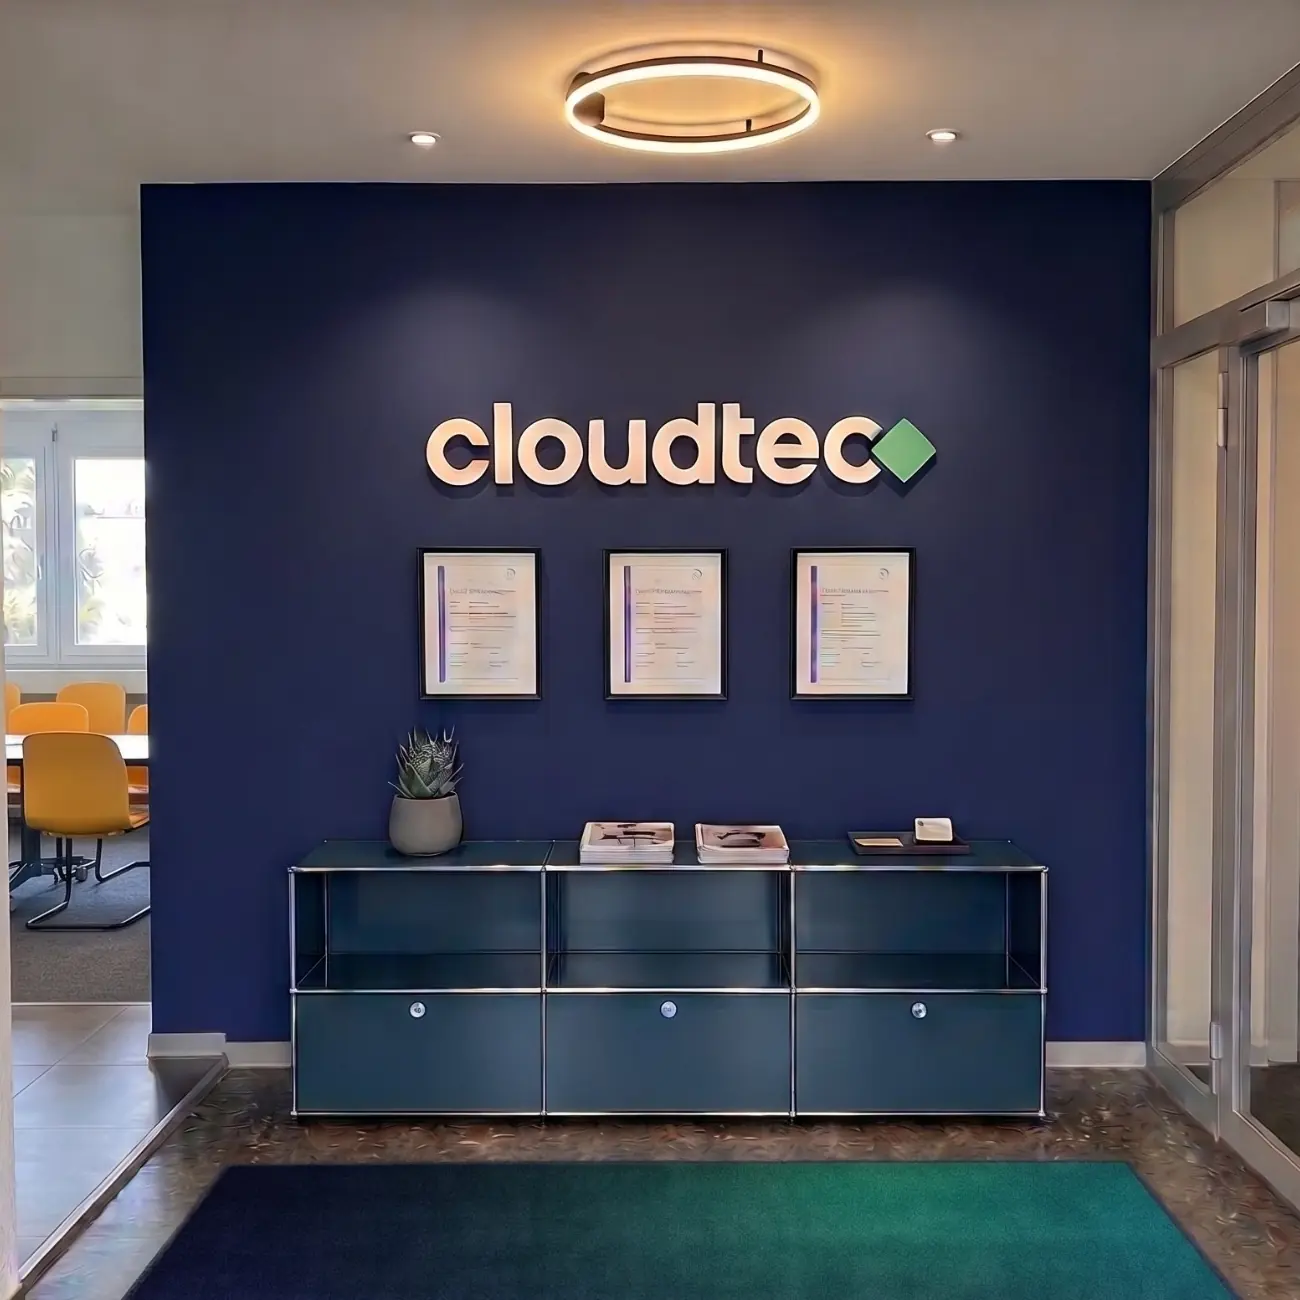
ISO/IEC 27001 is the internationally recognised standard for information security. We were certified by Attesta after an independent audit. We provide the scope and further evidence during security reviews.
Not every stage along the way was easy. One step at a time.
Every beginning is mostly theory
The start consisted mainly of reading and making sense of things. Before we could act, we had to understand the requirements of the standard and translate them to the reality of our own company. That was less spectacular than expected, but it laid the foundation for everything that followed.
It does not work without the whole team
An information security management system (ISMS) only works if everyone is on board. That is why we held numerous workshops with the team and the management. Together we defined security objectives, analysed risks openly and developed a shared understanding of which data assets we protect and why.
From doubt to confidence
To be honest: halfway through there were moments of uncertainty. The subject is complex, and at times we wondered whether we were still on the right track. That is where Kertos came in. With their expertise and a suitable platform, we found the thread again and gained confidence in our own processes. A big thank you to the Kertos team.
More than ticked checklists
Looking back, the ISMS was far more than preparation for an audit. We used the project to finally implement measures that had long been planned. Our internal processes are now more clearly defined and better secured than before.
The next audits
The certificate now hangs on the wall, and the badge sits in the footer of every page. The work does not end there: we have our ISMS reviewed regularly by independent third parties and keep developing the controls.
We are proud of the team that took this road with such persistence.
 Written by
Adrian Arnold
Senior Project Manager